Promise Theory Governance
Take a Product TourThe customer is a healthcare technology organization that runs AI agents across clinical operations and back-office workflows triaging alerts, reconciling records, and automating routine remediation under strict data-protection rules. To satisfy regulators, hospital partners, and its own board, the organization committed to certifying its AI management system against ISO/IEC 42001, the international standard for governing AI responsibly.
It had already adopted Scout to run those agents. What it needed next was proof: evidence that every agent behaved as intended, that controls were enforced rather than merely documented, and that an auditor could trace any AI decision back to the policy that governed it. Passing the audit, not just deploying agents, was the goal.
ISO/IEC 42001 asks an organization to show that its AI is governed continuously: risks managed, controls enforced, decisions accountable, and the whole AI lifecycle documented with evidence. For a fleet of autonomous agents acting thousands of times a day, the team's existing approach could not produce that proof.
The result was a familiar compliance trap: strong intentions, weak evidence. Certification demanded demonstrable AI controls and records, and the team had neither at the scale its agents operated.
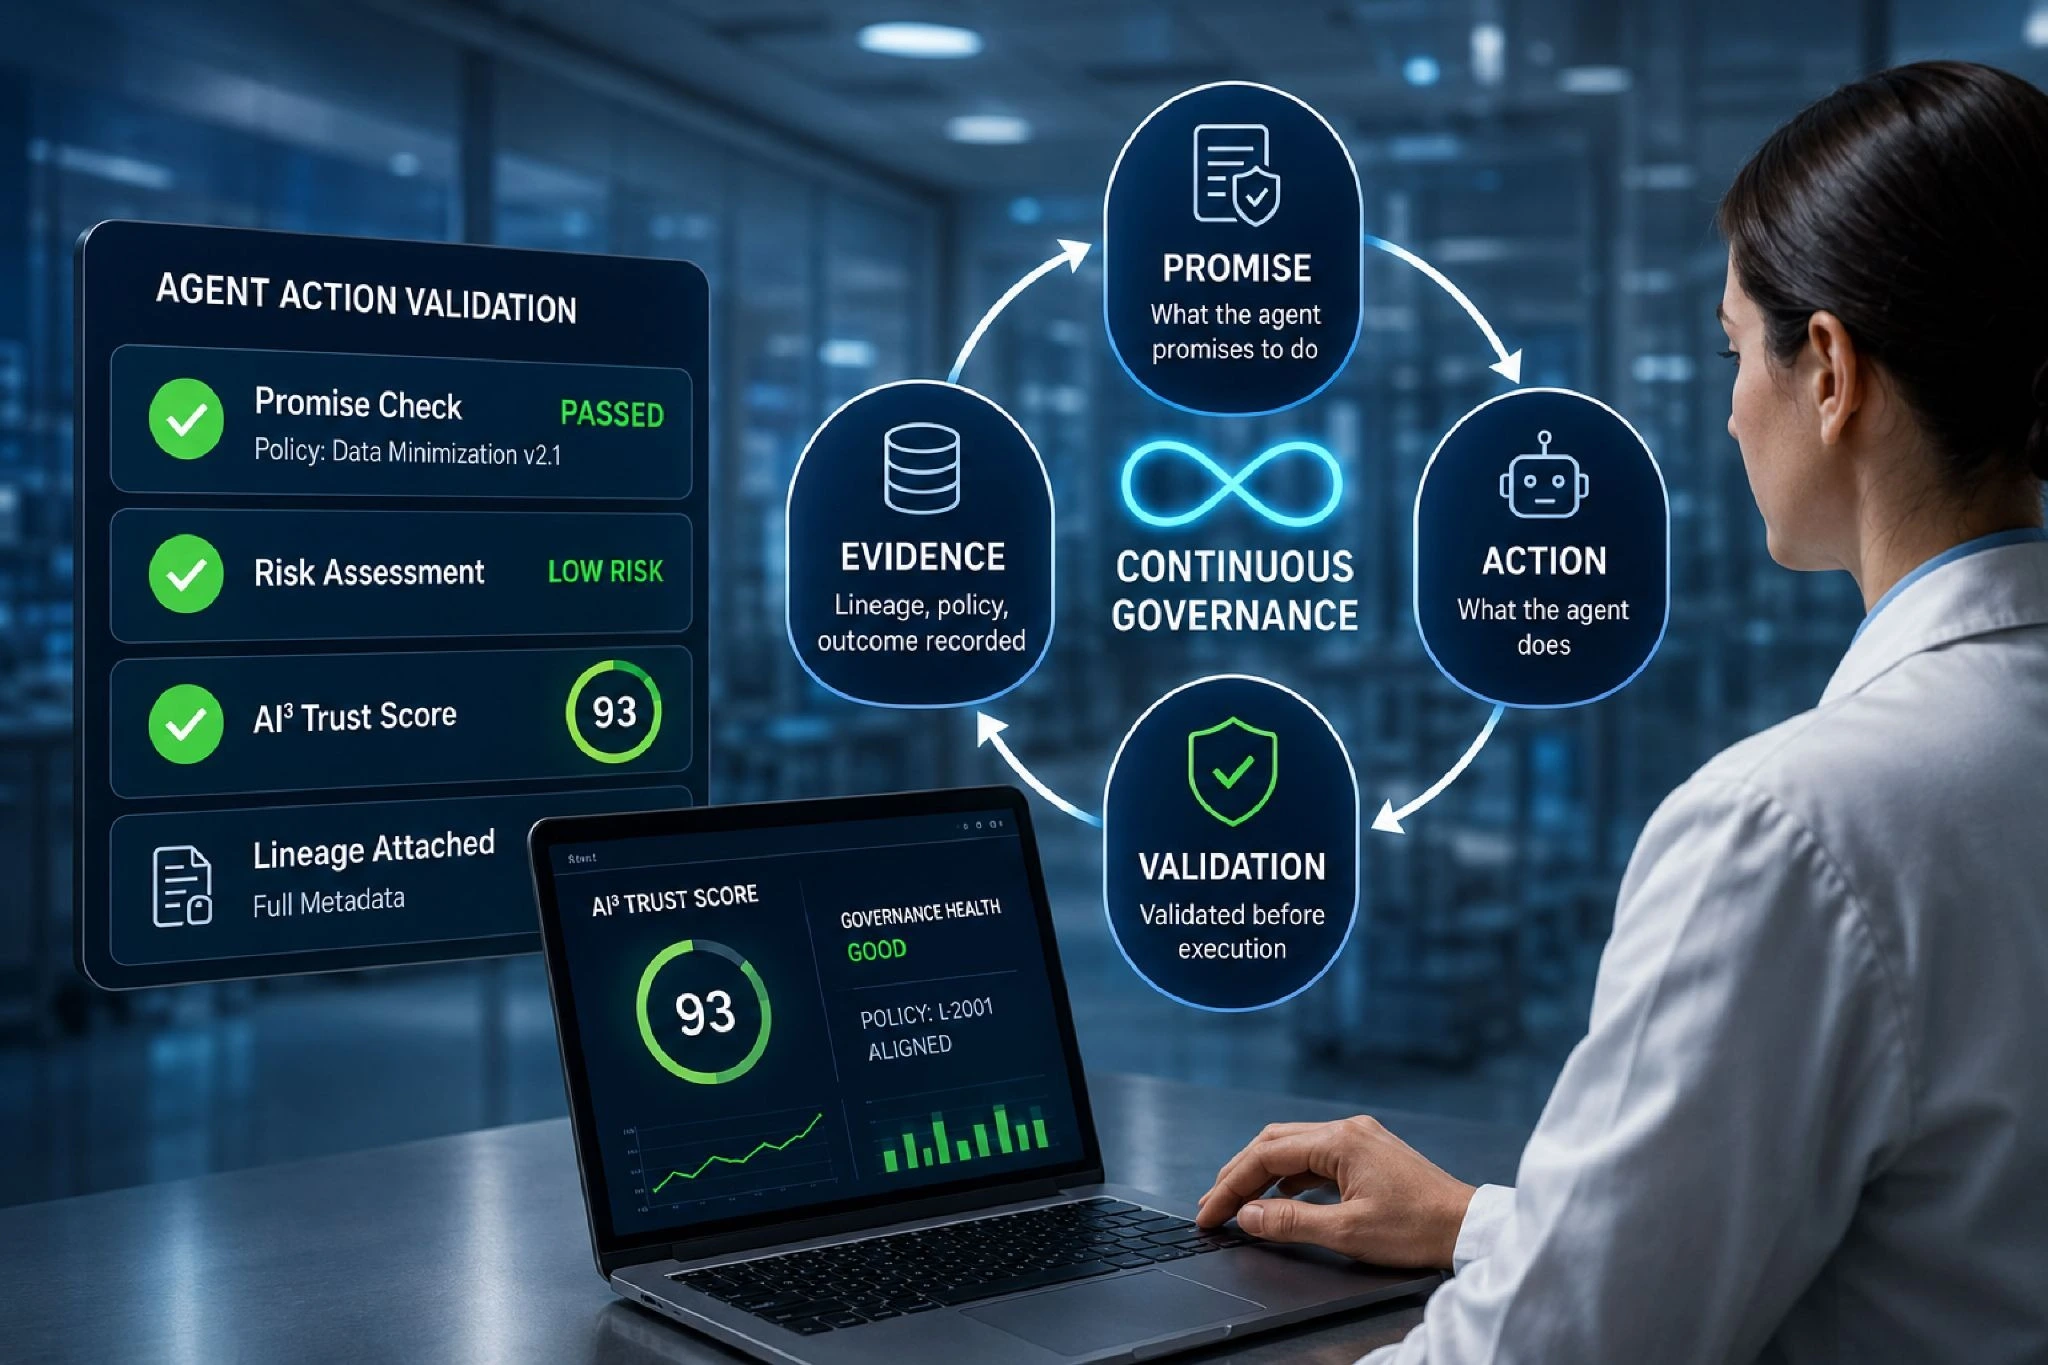
Scout's Promise Engine, built on Promise Theory, reframed governance as something provable. Each autonomous agent makes explicit, verifiable promises about its behavior, and every action is validated against that promise before it runs so the record of what an agent promised, what it did, and whether the two matched is generated automatically, as a byproduct of normal operation.
At the core, Scout's AI² Integrity Layer validates each action and produces a trust score for every decision. The Critic continuously evaluates behavior against ISO/IEC 42001 and flags governance or audit risk, attaching full metadata lineage to every promise. This turned AI compliance from a periodic scramble into continuous AI lifecycle governance: controls enforced at runtime, decisions traceable to their policy version, and evidence accumulating on its own. Every validation carried a lineage an auditor could follow the difference between claiming Responsible AI and demonstrating it.
Rollout was incremental, and the model mapped cleanly onto how the team already thought about scope and accountability:
Step 1 - Map controls to promises The team translated ISO/IEC 42001 controls into explicit agent promises and attached them during AI agent creation in Agent Studio, so teams could build AI agents with their controls provable from the start rather than bolted on later.
Step 2 - Enforce at runtime The Promise Engine validated every proposed action against its promise before execution, so controls were enforced in practice, not just declared.
Step 3 - Score continuously The Critic graded behavior against ISO/IEC 42001 and calculated an AI² trust score per agent, surfacing governance risk as it emerged rather than at audit time.
Step 4 - Generate evidence automaticallyEvery promise carried traceable lineage action, policy version, and outcome accumulating into a continuous, audit-ready record.
Step 5 - Route exceptions to humans The Bishop escalated genuine violations into a documented review workflow, giving auditors clear evidence of human oversight where it mattered.
| Traditional audit prep | Promise-based governance |
|---|---|
| Evidence gathered at audit time | Evidence generated continuously |
| Point-in-time review | Runtime enforcement and scoring |
| Controls declared on paper | Controls enforced at execution |
| Decisions hard to trace | Full lineage per decision |
Preparing for and clearing the audit changed shape entirely. (Figures are representative and should be validated against production data before external use.)
| Metric | Before | After |
|---|---|---|
| Audit preparation time | Weeks of manual evidence gathering | Reduced by ~60%, evidence continuous |
| Decision traceability | Partial, reconstructed by hand | Full lineage for every agent action |
| Governance findings at audit | Multiple gaps to remediate | Isolated exceptions, quickly closed |
| Control enforcement | Declared, unverified | ISO/IEC 42001-aligned, audit-ready |
Just as important, the evidence trail became a live asset rather than a quarterly project. Risk leaders gained a continuous view of which agents kept their promises, and audits became a byproduct of normal operation instead of a scramble at quarter's end.
The clearest lesson was that compliance is easiest when it is built in, not bolted on. Mapping ISO/IEC 42001 controls to agent promises from day one turned audits into a routine rather than an event. The team also learned that continuous beats point-in-time: a one-time review cannot govern systems that act thousands of times a day, but continuous promise verification can. And evidence should be a byproduct, not a project when every action carries its own lineage, AI accountability stops being something you assemble and becomes something you already have.
That is Trusted AI in practice: Responsible AI adoption backed by verifiable AI controls and AI risk management that hold up under audit. To see how Promise Theory governance produces continuous compliance, explore Scout's Promise Engine.


 No credit card required

